An Internal Policy Chatbot on AWS Bedrock
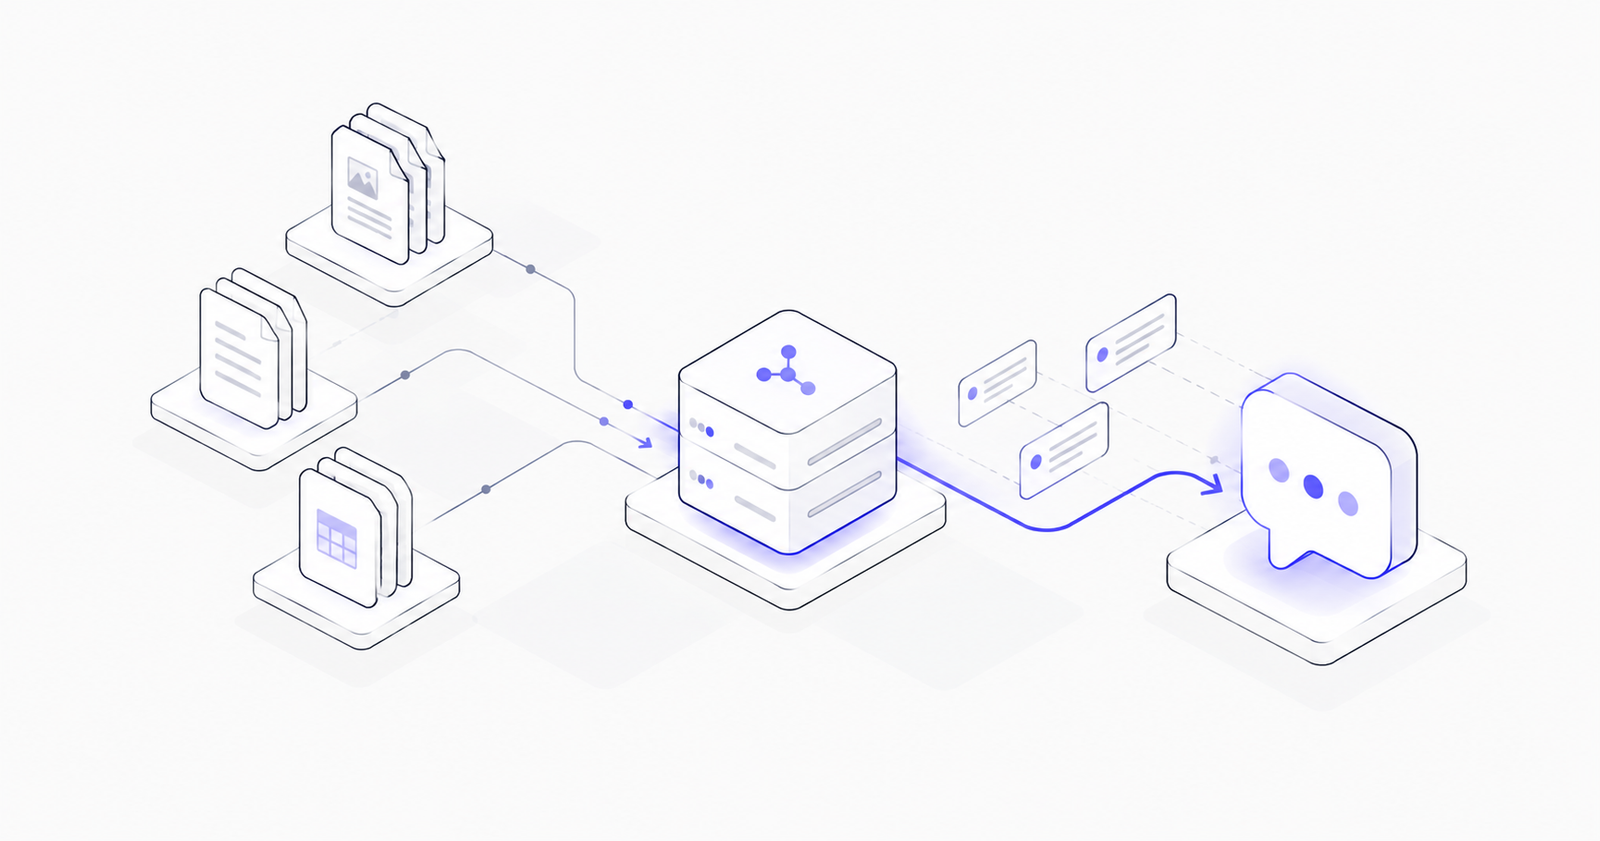
Built a retrieval-augmented chatbot on AWS Bedrock so employees could ask plain-language questions about internal company policy instead of searching through documents.
A mid-sized NBFC had no existing cloud footprint. We designed and stood up their entire AWS environment (compute, database, content delivery, cost controls and security) as one connected build.

The client was moving to AWS with no existing account structure, no established security baseline and no cost controls in place. Everything needed to be designed and built from zero, with the reliability and data-handling rigor financial services workloads require.
FAQ
For a mid-sized financial services workload like this, a properly sequenced build covering compute, database, CDN, IAM and cost controls typically takes a few weeks, not months — because security and cost visibility are designed in from day one instead of retrofitted later.
Retrofitting security after go-live means auditing infrastructure that's already carrying production traffic, which is riskier and slower. Building IAM roles, security groups and access policies into the initial design means there's no gap where the environment runs unprotected.
Yes, with the right configuration. AWS provides the compliance-ready building blocks — encryption, audit logging, access controls — but it's the customer's responsibility to configure them correctly for their regulatory requirements, which is exactly what this engagement was built around.
Keep reading

Built a retrieval-augmented chatbot on AWS Bedrock so employees could ask plain-language questions about internal company policy instead of searching through documents.

Standing management of a KYC company's ECS infrastructure: CI/CD security alerting, incident response, cost control, and log and secrets management, run as an ongoing operations engagement.
Get started
Let's design a cloud environment on AWS, Azure or GCP that is secure, scalable, reliable and cost-effective.