Logistics & Freight Forwarding (India)

Closing a Security Breach and Cutting Runaway Cost for a Freight Forwarding Company

A new client's AWS environment had a security group open to the internet and a compromised instance driving up cost. We closed the exposure, fixed the misconfiguration behind it, and brought cost back down.

  • 1 min read
  • AWS
  • Security Incident Response
  • Cost Optimization
  • EC2
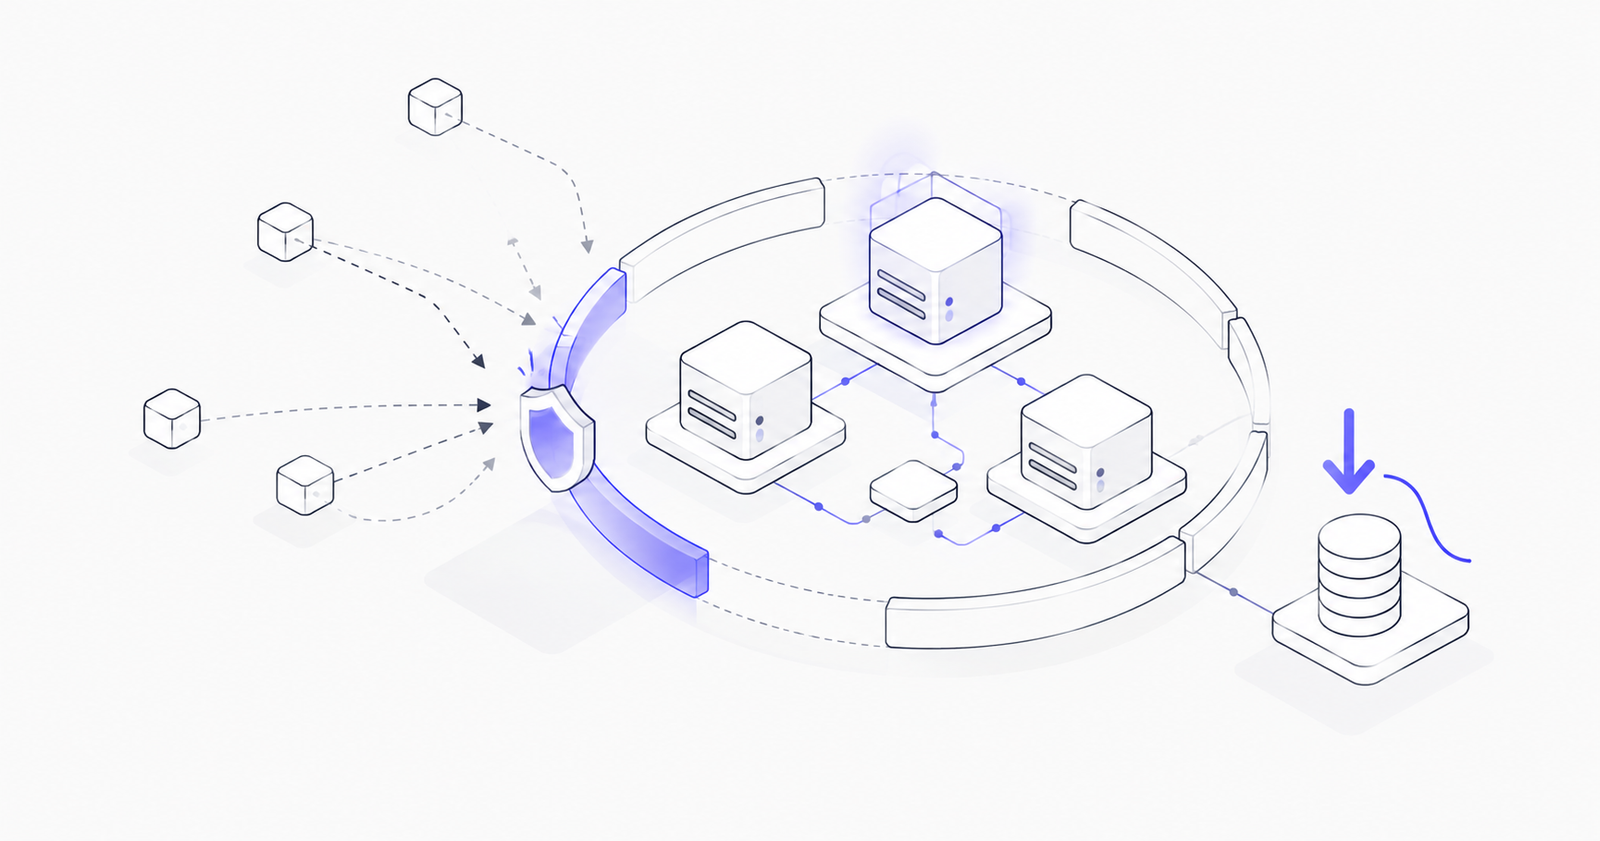
Isometric line drawing of a security ring closing on an indigo segment, with a downward arrow to a database.

Results at a glance

~30%Cost reduction after remediation

01The Challenge

A security group was left open to 0.0.0.0/0, and a t3a instance had been compromised as a result running unauthorized workloads that pushed CPU usage and cost well above baseline.

02What We Did

  • Locked down the exposed security group to remove public access to 0.0.0.0/0.
  • Investigated and removed the compromised workload running on the t3a instance.
  • Identified and fixed a CPU credit throttling misconfiguration on the instance that was contributing to the cost overrun.
  • Ran a full security audit across the account to check for other exposure before handing operations back to steady state.

03The Results

  • Public exposure closed and the compromised instance remediated, with no recurrence since.
  • Infrastructure cost reduced by roughly 30% once the misconfiguration and unauthorized workload were resolved.

FAQ

Common Questions

  • Through a full account audit that checked every security group, IAM policy and running workload — not just the specific instance that had already been compromised, since a real incident response has to rule out other open doors, not just close the one that's already been found.

  • The compromised instance was running unauthorized workloads that pushed CPU usage and cost well above baseline; once remediated, infrastructure cost dropped by roughly 30%, which is a rough proxy for how much the exposure had been costing.

  • A recurring audit process plus infrastructure-as-code practices so security-group rules are reviewed and version-controlled rather than changed ad hoc through the console.

Keep reading

More Case Studies

View All Case Studies
Isometric line drawing of a cloud stack: cloud, nodes, database and compute connected top to bottom.
NBFC / Financial Services

AWS Infrastructure, Built From the Ground Up for an NBFC

A mid-sized NBFC had no existing cloud footprint. We designed and stood up their entire AWS environment (compute, database, content delivery, cost controls and security) as one connected build.

Day 1Security and cost controls in place
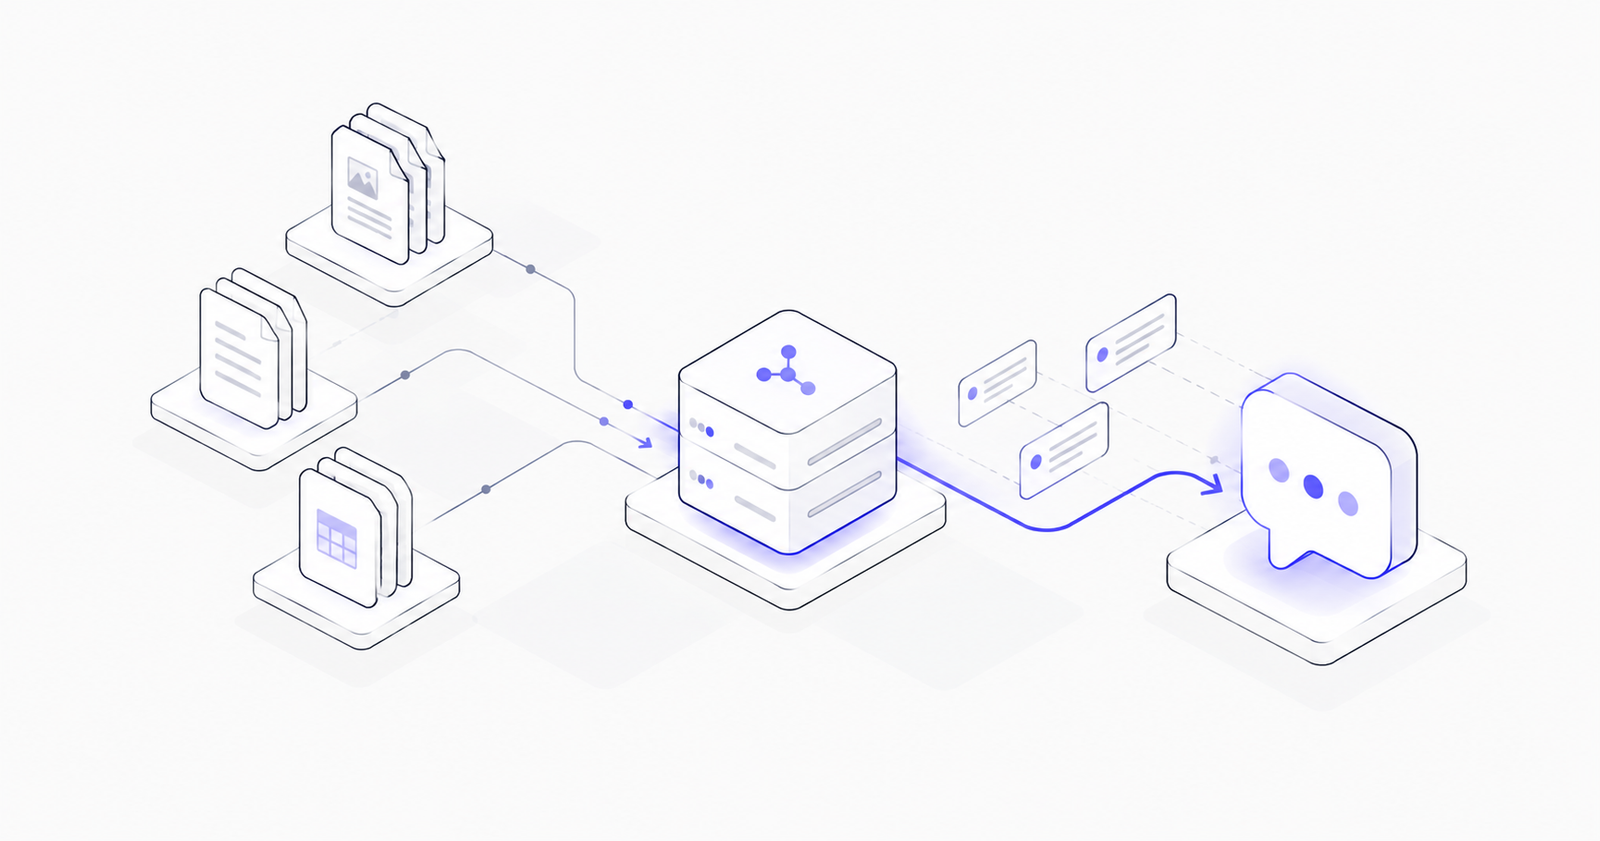
Isometric line drawing of documents flowing through a vector store into a chat bubble along an indigo path.
Startup / Internal Tools

An Internal Policy Chatbot on AWS Bedrock

Built a retrieval-augmented chatbot on AWS Bedrock so employees could ask plain-language questions about internal company policy instead of searching through documents.

InstantSourced answers to policy questions

Get started

Ready to Build on the Cloud?

Let's design a cloud environment on AWS, Azure or GCP that is secure, scalable, reliable and cost-effective.